In an era in which more than 11,000 publicly reported cyber incidents shook organisations across the European Union[1] in a single year – with DDoS attacks taking the top spot, while ransomware (malicious software) remains responsible for nearly half of all significant security incidents – the new Law on Information Security in Serbia arrives at a critically important moment. On the other side of the Atlantic, Verizon’s DBIR report[2] reveals that in 2023 alone more than 30,000 incidents compromising security were recorded, with nearly 10,000 cases confirmed as serious security breaches – exposing weaknesses across all industries. The cost of these incidents continues to rise – the average cost of a security incident amounts to USD 4.88 million in 2024[3].
For businesses, these figures point clearly to one thing: information security can no longer be treated as a side issue.
On 31 October 2025, the new Law on Information Security came into force, representing a key step towards improving the protection of information, infrastructure and digital systems in the Republic of Serbia.
Given the importance of digital transformation and the increasingly frequent threats in cyberspace, which can lead to immeasurable consequences, it was necessary to update the legal framework in this area in order to improve the security and resilience of information systems.
In addition, with the adoption of the NIS2 Directive, further alignment of the legislation of the Republic of Serbia with European Union regulations became necessary. This directive introduces significant novelties compared to the previous NIS Directive, primarily by expanding its scope and setting new standards in the field of cybersecurity.
At the same time, the accelerated development of artificial intelligence (AI) introduces new complexities in the domain of cybersecurity and data protection. AI-based systems are increasingly used to detect and respond to cyber threats, but at the same time they open up and create new vulnerabilities that require legal regulation. As artificial intelligence continues to shape the digital environment, ensuring a strong and adaptable regulatory approach is becoming even more important for protecting sensitive data and preserving trust in digital ecosystems.
Table of Contents
- The New Law on Information Security in Light of the Adoption of the NIS2 Directive
- What Are the Most Important Novelties in the New Law on Information Security?
- The Impact of the New Law on Information Security and the NIS2 Directive on Companies in Serbia
- Timely Monitoring of New Trends in Cybersecurity
- Frequently Asked Questions about the New Law on Information Security
1. The New Law on Information Security in Light of the Adoption of the NIS2 Directive
In short: In the process of EU alignment, the Republic of Serbia is obliged to harmonise its information security legislation with the 2022 NIS2 Directive. The new Law on Information Security expands and improves the existing provisions in order to respond to increasingly complex cyber challenges.
As cyber threats evolve and technologies change rapidly, there is a constant need to improve the existing legislation so that Serbia remains aligned with the latest international standards and keeps pace with regulatory trends in this area in a timely manner. In the process of fulfilling the requirements for full membership in the European Union, the Republic of Serbia is obliged to harmonise its legislation with the European Union acquis in the field of information security.
The European Union completed and revised its regulatory framework with the adoption of the Cybersecurity Act[4] in 2019, as well as the adoption of the new NIS2 Directive[5] in 2022, as part of the European Union’s broader effort to raise the level of protection of critical sectors and services across the Union, in view of the growing threat of cyber attacks.
The new Law on Information Security (hereinafter: the “New Law on Information Security”)[6], which aims to achieve alignment with the NIS2 Directive, seeks to expand and improve the existing provisions in order to adequately respond to the increasingly complex challenges in the cyber environment.
In order for the Republic of Serbia to successfully access the single European digital market, it is necessary to ensure regulatory and institutional conditions for the accelerated development of the electronic communications market in the Republic of Serbia, as well as to ensure that this development takes place in secure conditions, both for individuals and for companies.
2. What Are the Most Important Novelties in the New Law on Information Security?
In short: The New Law expands the scope to new sectors (healthcare, automotive industry, food production), redefines key entities as essential and important operators, introduces the Office for Information Security, a strict 24-hour incident notification deadline, incident categorisation, expanded powers of inspectors, certification and a new system of fines.
Below are just some of the numerous changes introduced by the New Law on Information Security.
The new regulations now cover entities in sectors that were previously not subject to statutory regulation: food production, the automotive industry, and others. Special attention will be paid to systems whose reliable operation is of key importance for the general welfare, in particular healthcare institutions, postal services, waste management services and the like.
A security breach of any of these vital infrastructures could not only halt essential services but also endanger the safety of individual citizens.
The Government of the Republic of Serbia has a deadline of one year from the date of entry into force of the New Law to adopt secondary legislation defining in more detail the criteria for classifying operators of ICT systems into the categories of essential and important. These criteria will be key to the practical application of the law, as they will precisely define which companies fall under the stricter and which under the lighter regime of obligations. It is expected that, in this process, the Government will be guided by standards from EU practice, in particular those prescribed by the NIS2 Directive, which take into account the size of the organisation, the number of employees and annual revenue, but also the importance of the services the company provides for the functioning of society and the economy. This would ensure that obligations are proportionate to the risks, while avoiding an excessive administrative burden for small and medium-sized enterprises.
Example: A company operating a payment platform and processing electronic transactions between users and banks, including card processing, payment verification and digital wallets, belongs to the financial services sector. Due to its key role in the functioning of payment operations, this system is considered an essential ICT system of special importance.
1. Redefining Key Entities
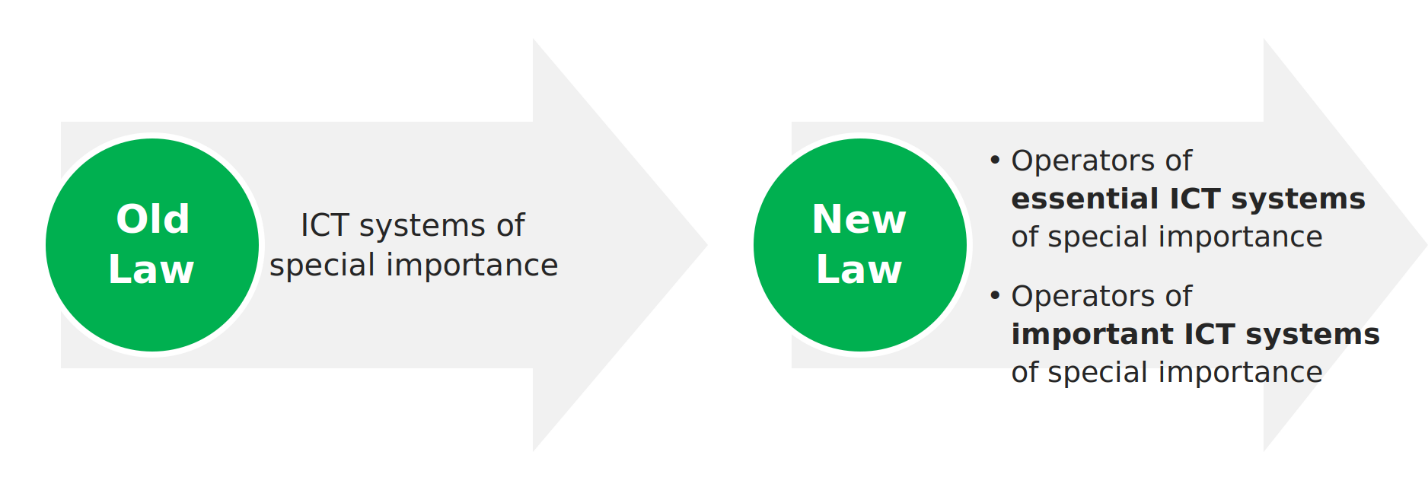
The New Law on Information Security identifies operators of information and communication systems (ICT)[7] of special importance and introduces their division into essential and important operators (jointly: the “Operators”).
Operators of essential ICT systems of special importance, which have inherited the role of the previous ICT systems of special importance, have now been extended to the sectors of water supply, wastewater management, management of ICT services provided to operators of essential ICT systems of special importance, as well as to providers of qualified trust services, DNS services and top-level domain name registry management, with the exception of root name server operators.
Example: A private hospital network uses a digital information system for managing patient records, appointment scheduling and network-connected diagnostic devices. Due to the processing of sensitive data and the impact on patient safety, the system is classified as an essential ICT system of special importance.
Example: A leading e-commerce platform, with a shopping website, APIs for merchant integration and payment services, is now, in line with the expanded scope of the term ‘information society services’, classified as an important ICT system of special importance. The company that owns this platform must comply with the New Law on Information Security.
For many private companies providing ICT support services to essential operators, the New Law means that they themselves automatically fall under the stricter regime of security obligations.
On the other hand, operators of important ICT systems of special importance include, among others, the sectors of postal services, the manufacture of computers, electronic and optical products, electrical equipment, machinery and equipment, motor vehicles and medical devices, as well as information society services within the meaning of the Law on Electronic Commerce, etc.
2. New Obligations for Operators
In addition to all the obligations under the current Law, Operators will now have an additional set of obligations, such as:
- Mandatory implementation of a risk assessment and adoption of a risk assessment act (reviewed at least once a year), i.e. a security assessment act,
- The obligation to submit notifications not only of incidents (as before), but also of serious threats to the ICT system of special importance.
3. Introduction of a New Supervisory Authority
The Office for Information Security (hereinafter: the “Office”) is introduced, which will take over the competences of the National CERT[8].
The Office will have the status of an independent regulatory agency responsible for coordinating incident response at the national level, improving the country’s preparedness and ensuring rapid intervention and remediation whenever a security event occurs.
4. Strict Incident Notification Deadline
Operators are required to submit, without delay and no later than 24 hours after learning about the incident, a notification of an incident that may have a significant impact on information security, in accordance with a strict formal incident update procedure. In addition, the information that Operators are required to provide when reporting an incident is now precisely prescribed.
This obligation is largely aligned with the data breach notification requirements under the General Data Protection Regulation (GDPR) and the Law on Personal Data Protection of the Republic of Serbia (LPDP). Under these laws, data controllers are obliged to notify the competent authority – such as the Commissioner in Serbia or the competent data protection supervisory authority in the European Union – of a personal data breach within 72 hours of becoming aware of it, unless the breach is unlikely to result in a risk to the rights and freedoms of individuals.
Similarly, just as Operators under the new cybersecurity framework are required to follow a structured incident notification procedure, data controllers under the GDPR and the LPDP must provide a precise set of information about the breach, including its nature, scope, possible consequences and the measures taken to mitigate the damage.
The alignment of incident notification requirements under cybersecurity and data protection regulations further highlights the growing regulatory focus on timely and transparent responses to security threats, ensuring both the resilience of information systems and the protection of individuals’ data.
5. Introduction of Incident Categorisation
Incidents in ICT systems of special importance that may have a significant impact on information security are classified according to the level of severity, taking into account the consequences of the incident, into the following categories:
- low,
- medium,
- high, and
- very high.
Depending on the categorisation of the incident, which will be regulated by separate secondary legislation, different obligations are imposed on Operators.
6. Expansion of the Powers of Information Security Inspectors
Information security inspectors have now been given additional powers enabling them to order the supervised entity to make information on non-compliance with the provisions of the law publicly available in a specific manner, where there is a justified public interest, as well as to order the appointment of a person with precisely defined powers within that entity, who will, for a certain period of time, supervise and monitor compliance with the provisions of the law and the imposed measures.
7. Introduction of Certification
One of the competences of the Office is the certification of ICT systems, ICT products, ICT processes and ICT services, with the exception of systems, products, processes and services intended for defence and security. This certification will not only contribute to improving security standards, but will also increase client trust and provide a competitive advantage for companies that opt for certification.
8. New System of Fines
The amount of fines depends on whether the operator of an ICT system of special importance is an essential or an important operator. Namely, the fines are higher for operators of essential ICT systems of special importance than for operators of important ICT systems of special importance, and amount to up to RSD 2,000,000.00 (approx. EUR 17,000) for operators of essential ICT systems of special importance, i.e. up to RSD 1,000,000.00 (approx. EUR 8,500) for operators of important ICT systems of special importance.
3. The Impact of the New Law on Information Security and the NIS2 Directive on Companies in Serbia
In short: Companies will face an expanded regulatory scope and increased compliance costs, but compliance will also bring benefits: greater trust of users and investors, a lower risk of incidents and easier cooperation with EU partners.
1. The Biggest Challenges
- Expansion of sectors covered by the Operators: By expanding the sectors to which it applies, the New Law on Information Security covers a significantly larger number of companies that will find themselves under increased legal scrutiny. This will impose new obligations, force them to engage actively in this area and affect their day-to-day operations – from data security to operational strategies in the event of incidents.
- Increased compliance costs: Compliance with the new regulations will bring increased costs for companies in the Republic of Serbia, as they will have to invest in stronger information system infrastructure, implement new protection systems, engage additional experts and train employees in order to meet the requirements of the new Law on Information Security. Local companies, especially those in critical sectors, are expected to have to invest in more sophisticated protection systems in order to ensure business continuity in the event of an incident.
2. Benefits
- Increased trust of users and investors: Compliance with modern regulations, as well as with international standards, can lead to greater security of user data, which contributes to strengthening the company’s reputation and the trust of users and investors, and builds confidence in the company’s operations. Whether a company is in the process of vendor assessment, considering merger and acquisition opportunities or attracting new investors, demonstrable compliance is a sign of good governance and instils confidence in all stakeholders at every stage.
- Reduced risks and challenges in business operations: Improving data and infrastructure security, as well as implementing and maintaining security systems, reduces incidents and risks to business operations. Strengthening security criteria reduces the risk of incidents, system damage and data leaks.
- Greater cooperation with EU partners: As the Republic of Serbia moves closer to alignment with EU standards, domestic companies will be able to cooperate more easily with companies from the European Union, as they will have harmonised security standards. This will reduce the risk of potential problems in international trade and business. In addition, by aligning with the NIS2 Directive, companies in the Republic of Serbia can become more competitive on the EU market and the international scene, thereby increasing the number of clients, consumers and users.
4. Timely Monitoring of New Trends in Cybersecurity
With the constant increase in the use of information and communication technologies (ICT) in everyday life, as well as the growing number of services offered to citizens electronically, it is necessary to respond to cybersecurity challenges in a timely manner. Likewise, constant monitoring of regulatory developments and the evolution of this dynamic sector is key to maintaining competitiveness on the market.
Compliance with the new Law on Information Security, and indirectly with the NIS2 Directive and its requirements, will be a serious challenge for companies, but also a significant step towards greater security in the digital environment. This will ensure safer use of digital services, reduce the risk of incidents and create conditions for attracting investment in the ICT sector.
Although companies in the Republic of Serbia will have to invest additional resources and meet new legal obligations, which will require adequate support and guidance, this process will contribute to their competitiveness, as well as to the trust of consumers and users, which is key to integration into the European economic area.
5. Frequently Asked Questions about the New Law on Information Security
Within what deadline are Operators required to report a security incident?
Operators are required to submit, without delay and no later than 24 hours after learning about the incident, a notification of an incident that may have a significant impact on information security, in accordance with a strict formal notification procedure.
Which new sectors are covered by the New Law on Information Security?
The new regulations now cover entities in sectors that were previously unregulated, such as food production, the automotive industry and healthcare, with special attention paid to healthcare institutions, postal services and waste management, given their importance for the general welfare of citizens.
What is the difference between essential and important ICT operators?
Operators of essential ICT systems of special importance are subject to a stricter regime of obligations, including compliance checks of protection measures twice a year and higher fines (up to RSD 2,000,000), while operators of important ICT systems have a lighter regime of obligations and lower fines (up to RSD 1,000,000).
What fines are prescribed by the New Law on Information Security?
Fines amount to up to RSD 2,000,000.00 (approx. EUR 17,000) for operators of essential ICT systems of special importance, i.e. up to RSD 1,000,000.00 (approx. EUR 8,500) for operators of important ICT systems of special importance.
Which authority takes over the competences of the National CERT?
The Office for Information Security is introduced, which will have the status of an independent regulatory agency responsible for coordinating incident response at the national level, as well as for the certification of ICT systems, products, processes and services.
Legal Notes and Sources
- European Union Agency for Cybersecurity (ENISA), threat report.
- Verizon, 2024 Data Breach Investigations Report.
- IBM, Cost of a Data Breach Report 2024.
- Regulation (EU) 2019/881 of the European Parliament and of the Council of 17 April 2019 on ENISA (the European Union Agency for Cybersecurity) and on information and communications technology cybersecurity certification, and repealing Regulation (EU) No 526/2013 – eur-lex.europa.eu.
- Directive (EU) 2022/2555 of the European Parliament and of the Council of 14 December 2022 on measures for a high common level of cybersecurity across the Union, amending Regulation (EU) No 910/2014 and Directive (EU) 2018/1972, and repealing Directive (EU) 2016/1148 – eur-lex.europa.eu.
- Law on Information Security (Official Gazette of the RS, No. 91/2025).
- Information and communication system (abbreviated: ICT system).
- Centre for the prevention of security risks in ICT systems.
Updated by: Marija Veselinović, Senior Associate · View profile
Related people